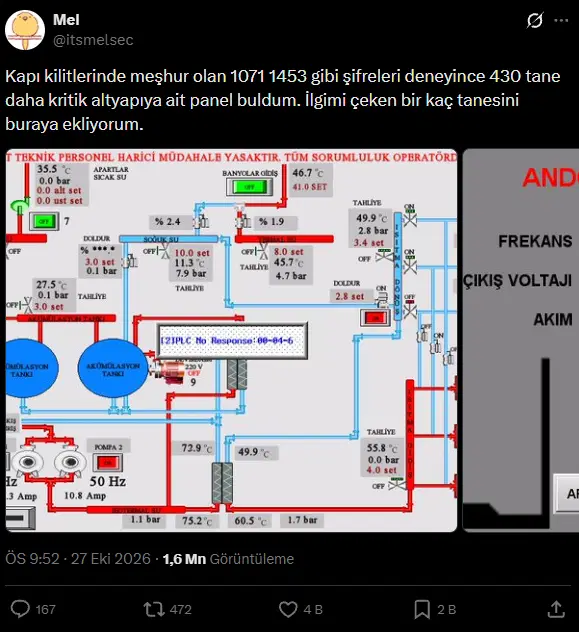
The cybersecurity of critical infrastructure in Turkey, such as water, wastewater, and valve control systems, has come to the fore with a new allegation. A cybersecurity researcher using the username “itsmelsec” on social media claimed to have identified 430 new industrial control panels that they allege are exposed to the internet, and that they were able to access some of them using easily guessable passwords.
According to the researcher's post, the passwords tested included the number sequences “1071” and “1453,” which are frequently used in Turkey. The shared screenshots show control interfaces containing information such as pump operating status, tank levels, pressure values in pipelines, and valve positions.
WHAT DO THE ALLEGATIONS COVER?
The systems claimed to be included in the posts range from water pumps, wastewater facilities, and drinking water lines to hot water systems, pressure stabilization valves, and regulator control screens. Although some interfaces appear to have options for starting-stopping pumps or opening-closing valves, this does not in itself prove that the researcher was able to perform a physical operation on the systems in question.
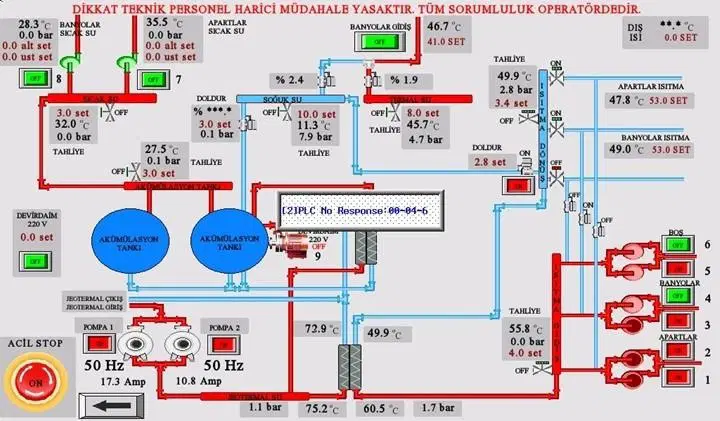
It was reported that one of the images contained the ASKİ logo and the phrase “Kuşadası Yeniköy Wastewater Pumping Station,” and that the panel monitored the booster pump pool level and the operating frequencies of three pumps. Another screen featured a control interface stated to belong to a pressure stabilization valve room, along with the İLBANK and ASKİ logos.
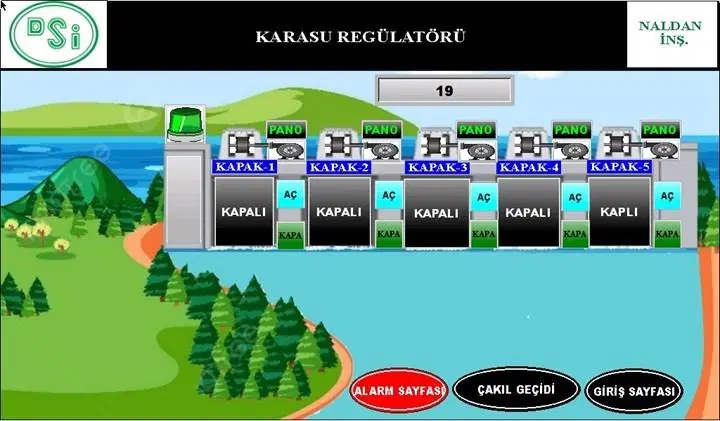
Among the images published by the researcher is a screen titled “Karasu Regulator” bearing the DSI logo. This panel shows the status of five gates and open-close options. Another image titled “Şanlıurfa Organized Industrial Zone Valve Control System” also shows the status of incoming and outgoing water valves and control buttons.
Industrial control systems are used to remotely manage physical processes such as pumping, storing, and treating water, and monitoring valves on lines. If these systems are exposed to the internet and are not protected by strong authentication methods, the risk of unauthorized access increases. The use of easily guessable or default passwords is also considered one of the main factors that amplify this risk.
WHAT HAD ASKİ SAID BEFORE?
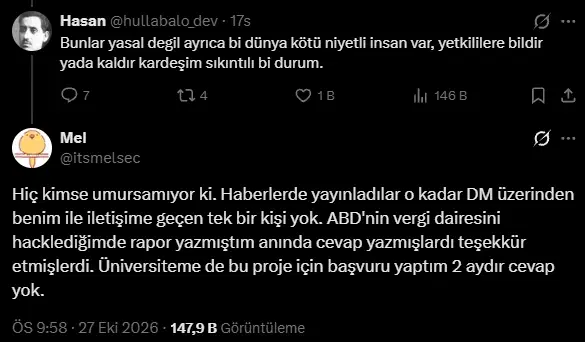
Following the allegations, it has not yet been independently verified whether the shared screens actually belong to the relevant public institutions and to what extent the access level goes. The researcher also claimed that no institution had contacted them regarding the systems they said they had exposed.
ASKİ General Manager Memduh Aslan Akçay had stated in a previous statement regarding similar allegations that the shared screenshots did not match the systems within ASKİ. Akçay had said, “There is no security vulnerability, but we continue to carry out our checks to ensure our security. We are aware of how important cybersecurity is and we are trying to keep security at the maximum level.”
Whether the institutions whose names or logos appear in the new posts will make a separate statement regarding the allegations has become a matter of curiosity.
News Source: 12punto