

RatHat alert on Android: Bank passwords under threat
It has been reported that a piece of malware called RatHat, which targets Android devices, can steal bank login credentials, one-time passwords, screen lock patterns, and PINs.


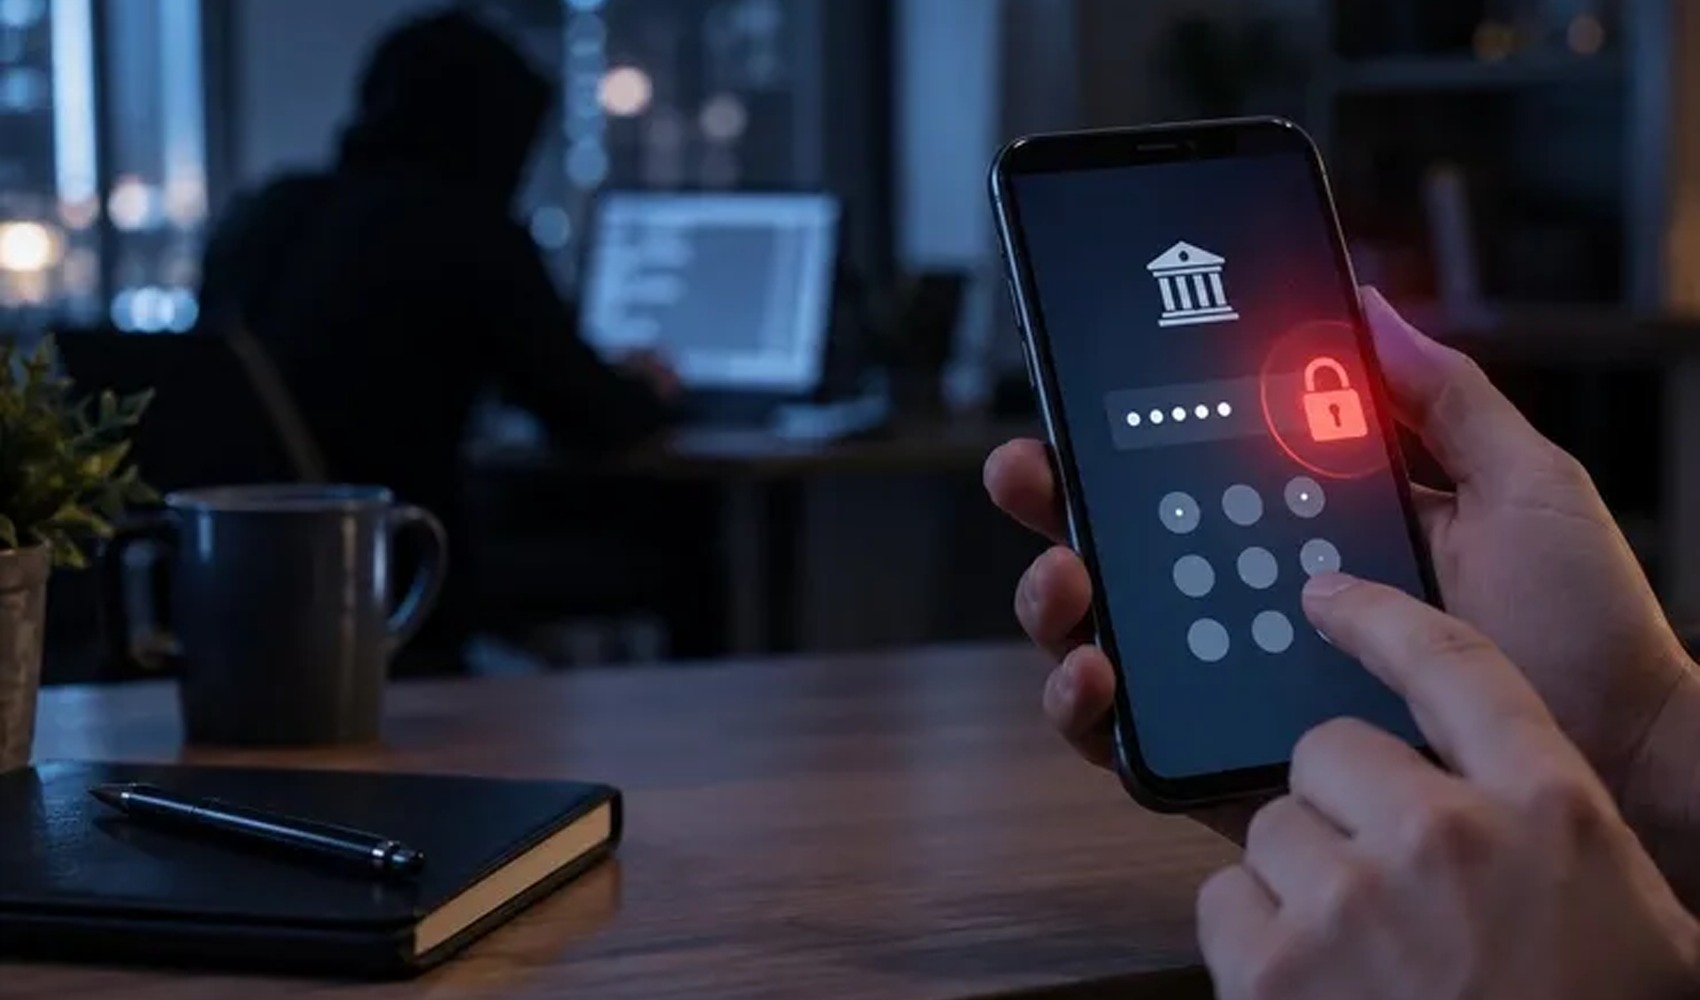
A new banking trojan targeting Android devices has emerged. It has been reported that the malware, dubbed "RatHat," is capable of seizing information that plays a critical role in accessing users' financial accounts.
The software in question is said to target data such as bank login credentials, one-time passwords, screen lock patterns, and PIN codes. Such information poses a serious risk, as it allows attackers to gain access to both banking applications and sensitive data within the device.
In line with general security recommendations from experts, it is important for Android users to download applications only from trusted sources, avoid clicking on unknown links, and regularly check application permissions. Keeping device and application updates current is also among the fundamental measures against potential security vulnerabilities.
Users who notice suspicious notifications, unexpected login alerts, or unusual account activity during banking transactions are advised to contact their banks without delay and have their device security checked.
News Source: 12punto
Most Read
Transaction suspension decision from MASAK
'Direct dialogue between Erdoğan and Trump has created room for maneuver'
Armed attack on a school in Manisa: 11 students injured, 2 in critical condition
Will the Yemen tender fall to Turkey?
A call from Şamil Tayyar following the fund operation
First appearance by Ali Koç in a long time
Do we have to buy a phone?
Partners of famous Istanbul shopping mall detained
The real test for the Left Party begins now
6-month driving ban for Mohamed Salah